Security research, bug bounty, and technical writeups.
Dissecting CVE-2026-34530: Stored XSS via text/template Branding injection
For this blog, we’ll look at CVE-2026-34530: Stored Cross-Site Scripting via text/template branding injection and trace it back to the source code to understand exactly where and why the vulnerability exists. We have two keyword in the title: Stored Cross-Site Scripting text/template branding injection The blog assumes you at least have a basic understanding of Cross-Site Scripting. You may learn more about it at What is cross-site scripting (XSS)? We’ll come down to the second keyword: text/template branding injection ...
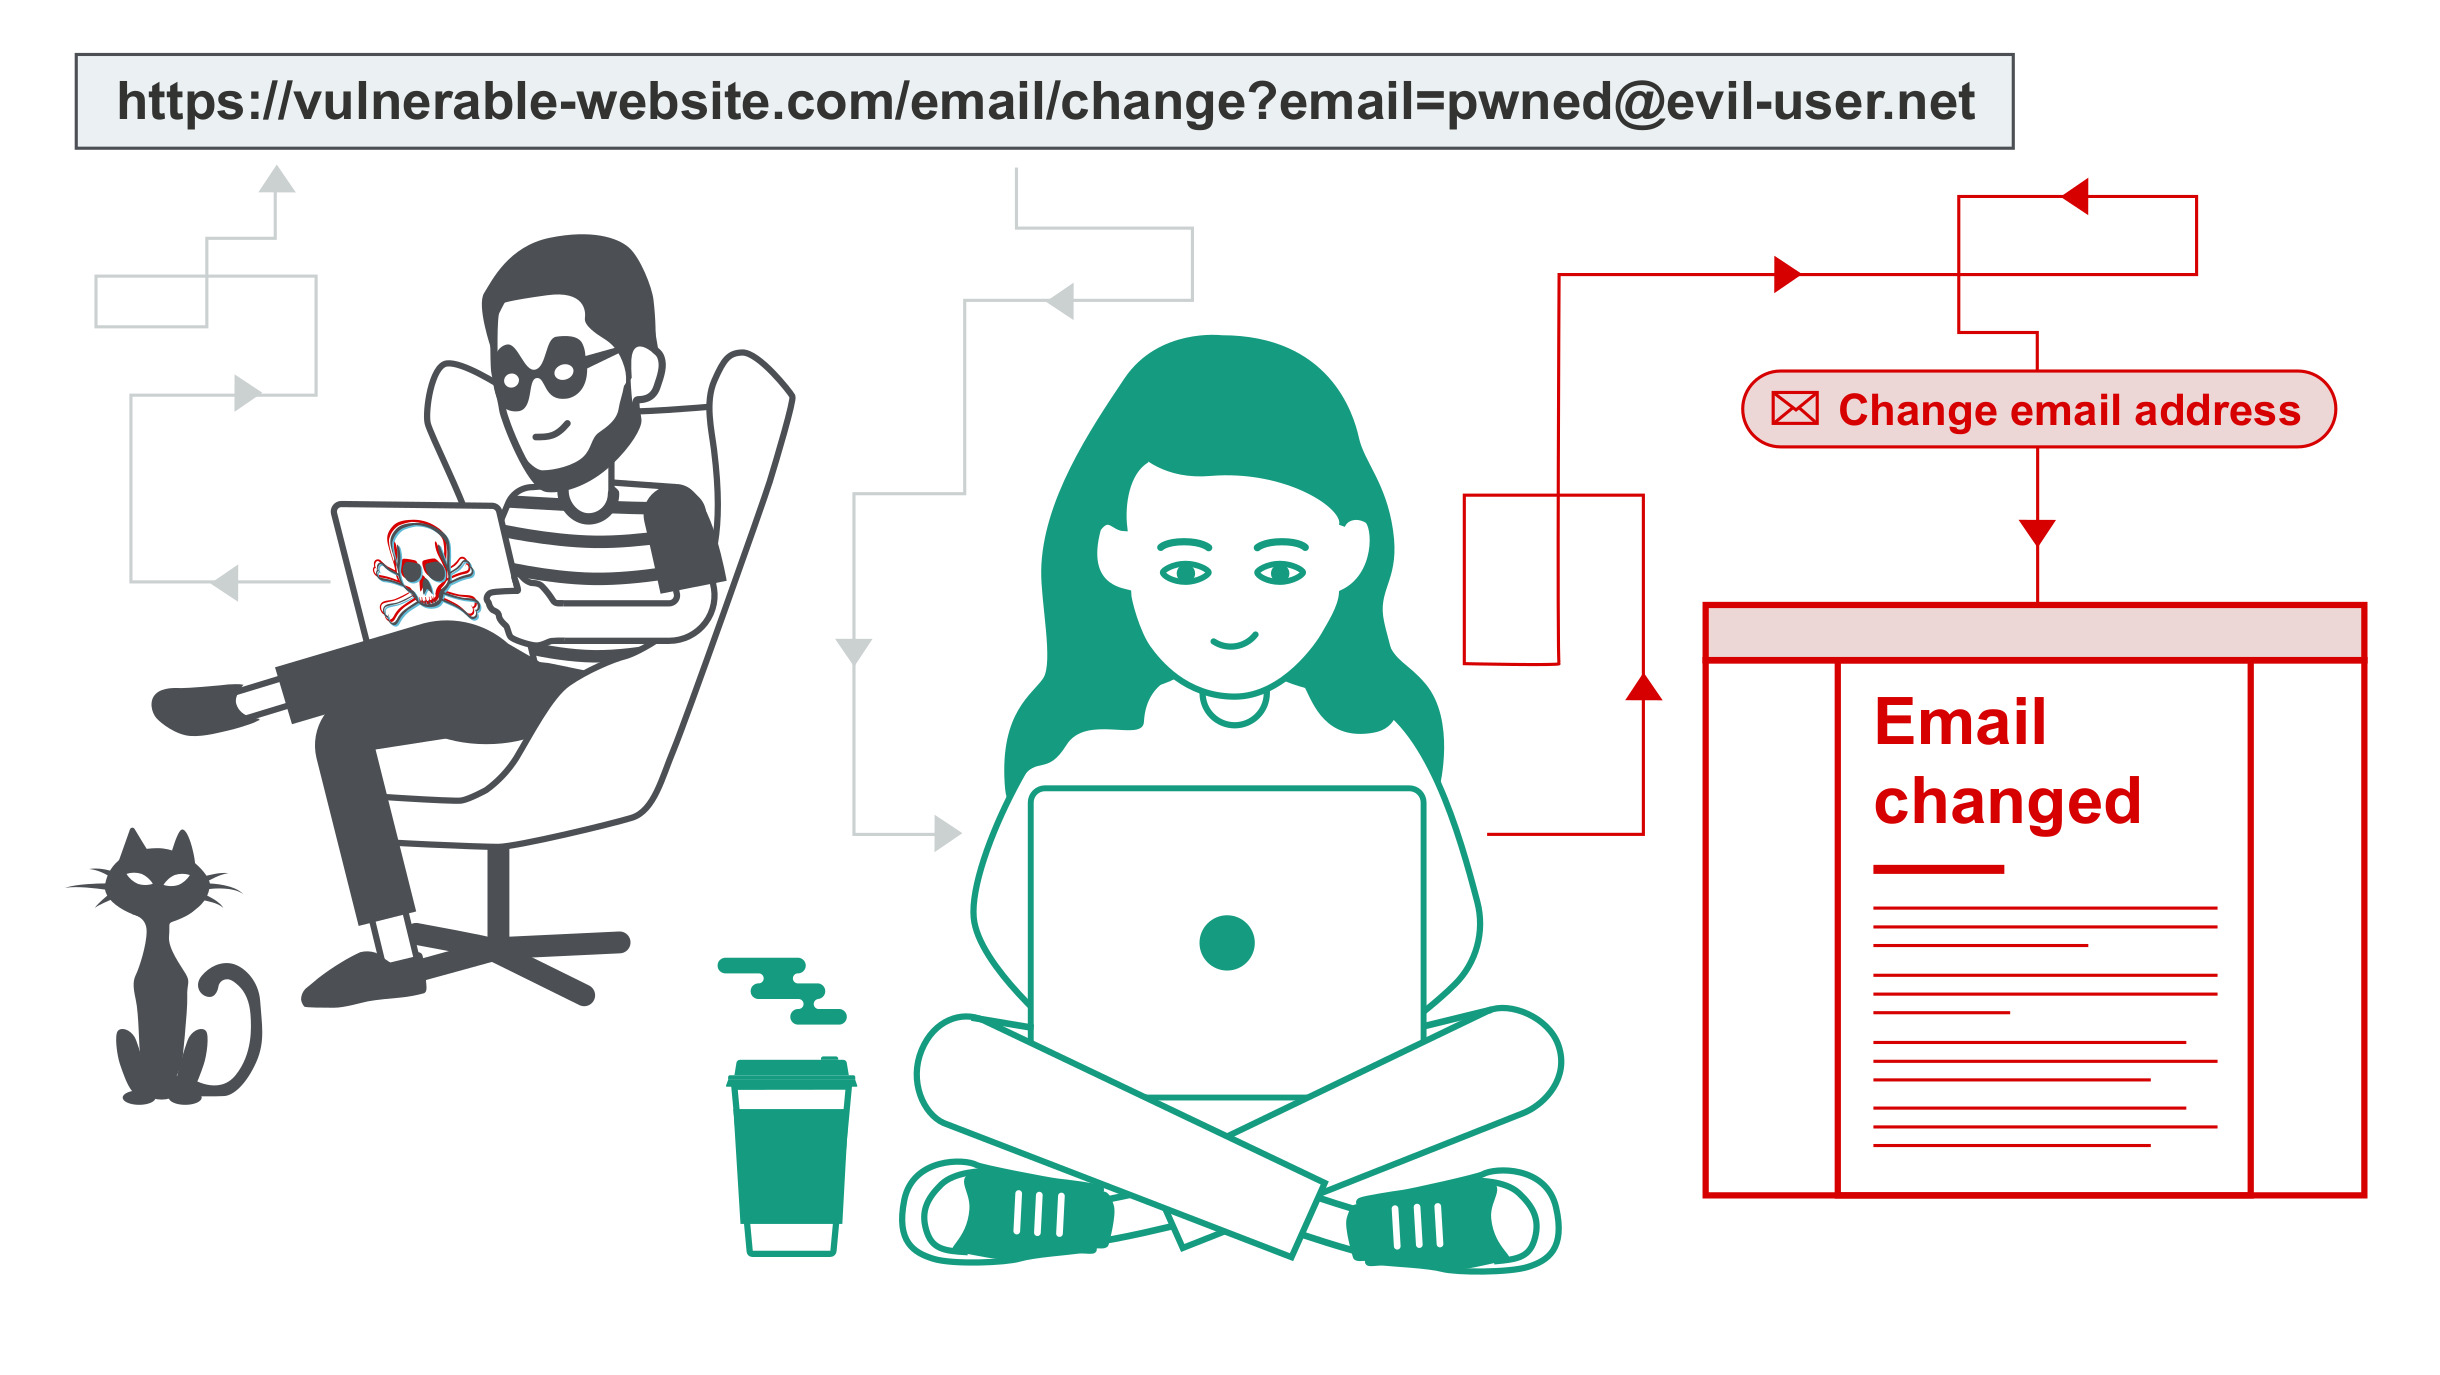
CSRF on Password Reset Link leading to account takeover.
Have you ever thought of testing for CSRF vulnerability on a password reset link? You might not have, because we generally believe that it is not possible, as the password reset link itself contains a reset token which acts as an alternative for a CSRF token. I, too, once shared this assumption, but recently I encountered a CSRF vulnerability on a password reset link on a popular site. Since the vulnerability is still not patched, let’s refer to it as https://target.com ...
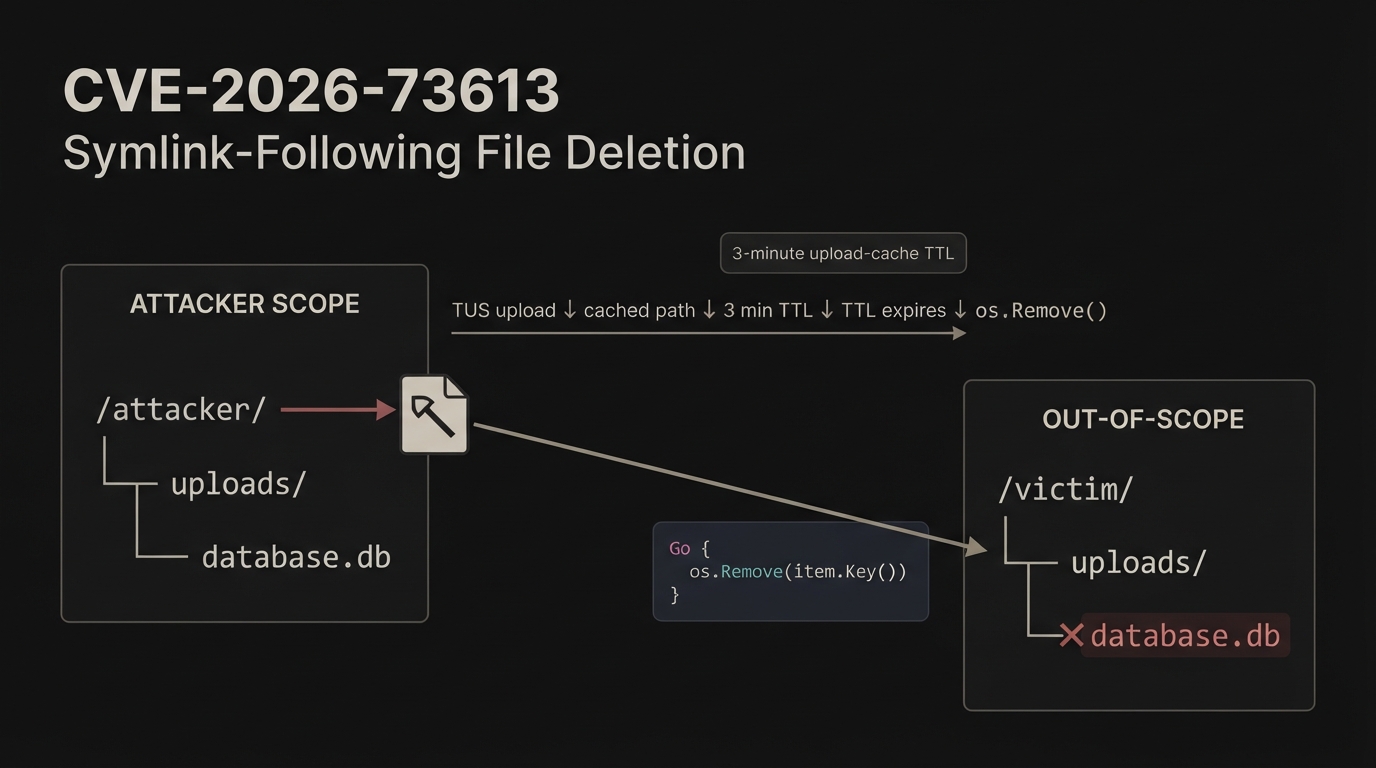
Dissecting CVE-2026-73613: File Deletion via Symlink in TUS
For this blog, we’ll look at CVE-2026-73613: Out-of-scope file deletion via symlink-following delete in TUS upload-cache eviction and trace it back to the source code to understand exactly where the vulnerable behavior comes from and how it can lead to file deletion outside the intended directory. We have 3 keywords in the title: Out-of-scope file deletion symlink TUS upload-cache eviction 1. Out-of-scope file deletion This one is pretty simple. Consider the following scenario: ...